
What Does a WordPress Security Audit Include in 2026?
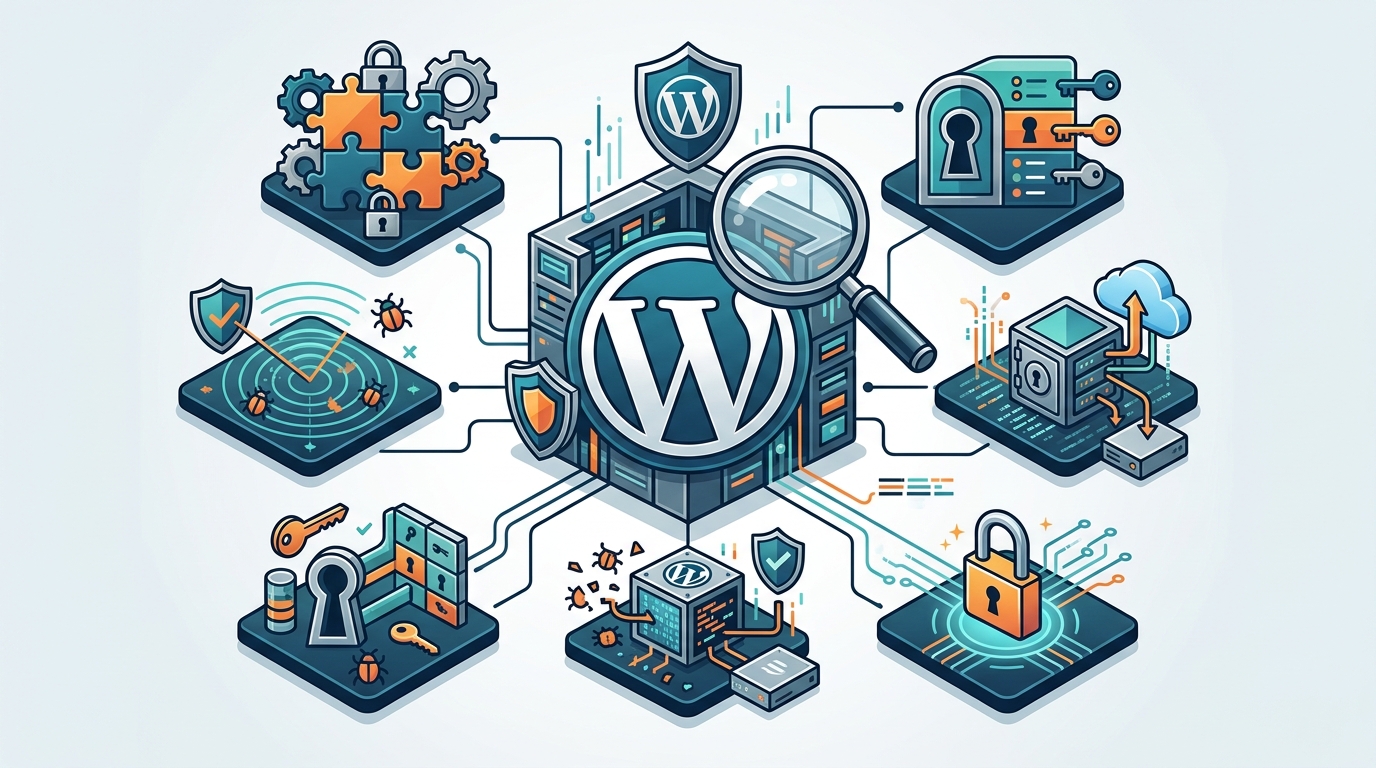
A WordPress security audit is a structured evaluation of a site's configuration, code, access controls, and infrastructure to identify vulnerabilities before attackers exploit them. This guide details the six core components of a professional audit: configuration hardening, vulnerability scanning, user access control, malware detection, backup procedures, and SSL/TLS security. It explains how Računalničar, Sebastijan Bandur s.p. approaches these tasks using modern tools and methodologies.
WordPress Configuration Hardening
Configuration hardening is the process of modifying system settings to reduce the attack surface of a web application. For WordPress, this involves locking down the core files, disabling unnecessary features, and enforcing strict permissions. A secure configuration is the foundation upon which all other security measures rely.
Core File Integrity and Permissions
Attackers often attempt to modify core WordPress files to inject malicious code. A robust audit verifies that file permissions are set to the minimum required for operation. Typically, directories should be set to 755 and files to 644. The wp-config.php file should be set to 440 or 400 to prevent unauthorized reading or writing. If a file is writable by the web server user, it is a critical vulnerability.
Disabling Unnecessary Features
Every feature in WordPress is a potential entry point. A security audit checks for and disables features that are not in use. This includes the XML-RPC interface, which is often targeted for brute-force attacks and distributed denial-of-service (DDoS) attacks. It also involves disabling the file editor in the admin dashboard and removing the WordPress version number from the source code to prevent attackers from targeting known vulnerabilities in specific versions.
Security Headers
Vulnerability Scanning
Vulnerability scanning is the automated or semi-automated process of identifying known security weaknesses in a system. In the context of WordPress, this involves checking the core software, themes, and plugins against databases of known vulnerabilities. A scan provides a snapshot of the current security posture and highlights areas that require immediate attention.
Core, Theme, and Plugin Scanning
WordPress sites are only as secure as their weakest component. While the core software is regularly updated and patched, third-party themes and plugins are often the source of vulnerabilities. A comprehensive scan checks every installed plugin and theme against the WordPress.org repository and other vulnerability databases. It identifies outdated versions, abandoned plugins, and known exploits. For example, a plugin that has not been updated in over a year is a high-risk component, even if no specific vulnerability is currently listed.
Dynamic vs. Static Analysis
Static analysis examines the code without executing it, looking for patterns that indicate potential vulnerabilities. Dynamic analysis, on the other hand, interacts with the running application to identify issues that only appear during execution. A professional audit, such as the one offered by Računalničar, combines both approaches. It uses tools like Kali Linux and WebTesterAI MCP to perform deep, agent-orchestrated scans that go beyond simple signature-based detection. This allows for the identification of logic flaws and business logic vulnerabilities that automated scanners might miss.
OWASP Top 10 Alignment
The Open Web Application Security Project (OWASP) Top 10 is a standard document that lists the most critical security risks to web applications. A quality audit maps its findings to the OWASP Top 10 categories, such as Broken Access Control, Cryptographic Failures, and Injection. This provides a clear framework for understanding the severity and impact of each finding. It also ensures that the audit covers the most common and dangerous attack vectors.
User Access Control
User access control is the mechanism that determines who can view or use resources in a system. In WordPress, this is managed through the role and capability system. A security audit reviews all user accounts, their assigned roles, and the permissions associated with those roles. The goal is to enforce the principle of least privilege, where each user has only the minimum access necessary to perform their job.
Role and Capability Review
Account Hygiene and MFA
Account hygiene involves managing the lifecycle of user accounts. An audit identifies and removes inactive, orphaned, or duplicate accounts. It also checks for accounts that have not been used in a significant period. Multi-Factor Authentication (MFA) is a critical control that adds an extra layer of security to the login process. An audit verifies that MFA is enforced for all privileged users, such as Administrators and Editors. Without MFA, a compromised password grants full access to the site.
Login Security
The login page is a primary target for brute-force attacks. An audit evaluates the security of the login process. This includes checking for rate limiting, account lockout policies, and the use of secure login URLs. It also verifies that the login page is protected by SSL/TLS and that session management is secure. Weak login security is one of the most common ways that WordPress sites are compromised.
Malware Detection
Malware detection is the process of identifying malicious code that has been injected into a website. Malware can be introduced through vulnerable plugins, compromised credentials, or direct attacks. It can range from simple spam links to sophisticated backdoors that give attackers persistent access. A security audit includes a thorough malware scan to ensure the site is clean.
File System Scanning
Code Review and Integrity Checks
Some malware is obfuscated or encoded to evade simple signature-based scans. A code review involves manually inspecting suspicious files for malicious logic. This is a time-consuming but essential part of a deep audit. Integrity checks verify that core files have not been modified by comparing their checksums against the original WordPress distribution. Any discrepancy indicates a potential compromise.
Network and Traffic Analysis
Malware often communicates with external command-and-control (C2) servers. Network analysis monitors outbound traffic from the web server to identify connections to known malicious IP addresses or domains. It can also detect data exfiltration, where sensitive data is being sent out of the site. This layer of detection is crucial for identifying advanced persistent threats (APTs) that may have evaded file-based scans.
Backup Procedures
Backup procedures are the set of practices used to create and store copies of data to protect against loss. In a security context, backups are a critical recovery mechanism. If a site is compromised, a clean backup allows for a rapid restoration. A security audit evaluates the effectiveness, frequency, and security of the backup process.
Frequency and Retention
The frequency of backups determines how much data can be lost in the event of a failure or attack. A daily backup is a common minimum standard for active sites. The audit verifies that backups are being created as scheduled and that they are successful. It also reviews the retention policy, which determines how long backups are kept. A robust retention policy ensures that there are multiple clean backups available for restoration, allowing for the rollback to a point in time before a compromise occurred.
Backup Security and Storage
Backups are a valuable target for attackers. If a backup is stored on the same server as the live site, it can be encrypted or deleted during a ransomware attack. An audit verifies that backups are stored off-site, ideally in a different geographic location or cloud provider. It also checks that backups are encrypted both in transit and at rest. Access to backups should be restricted to authorized personnel only, with strict access controls in place.
Restoration Testing
SSL/TLS Security
SSL/TLS security is the use of encryption protocols to secure data in transit between a user's browser and the web server. SSL (Secure Sockets Layer) and its successor, TLS (Transport Layer Security), are the standards for encrypting web traffic. A security audit evaluates the configuration and strength of the SSL/TLS implementation on a WordPress site.
Certificate Validity and Chain
A valid SSL certificate is the first line of defense. An audit verifies that the certificate is not expired, that it matches the domain name, and that it is issued by a trusted Certificate Authority (CA). It also checks the certificate chain to ensure that all intermediate certificates are present and valid. An expired or misconfigured certificate will trigger browser warnings, eroding user trust and potentially indicating a security issue.
Protocol and Cipher Suite Strength
Not all SSL/TLS configurations are equally secure. Older protocols like SSLv3 and TLS 1.0 are considered insecure and should be disabled. An audit checks that only modern, secure protocols like TLS 1.2 and TLS 1.3 are enabled. It also reviews the cipher suites in use, ensuring that weak or broken ciphers are not allowed. Strong cipher suites provide robust encryption and forward secrecy, protecting data even if the private key is compromised in the future.
HSTS and Redirects
HTTP Strict Transport Security (HSTS) is a header that instructs browsers to only connect to the site over HTTPS. An audit verifies that HSTS is enabled and configured with an appropriate max-age. It also checks that all HTTP requests are correctly redirected to HTTPS. This prevents man-in-the-middle attacks where an attacker intercepts unencrypted traffic. Proper SSL/TLS configuration is essential for protecting sensitive data, such as login credentials and payment information.
Key Takeaways
- Vulnerability Scanning: Regularly scan core, themes, and plugins for known vulnerabilities. Use dynamic and static analysis to identify logic flaws.
- User Access Control: Enforce the principle of least privilege. Review roles and capabilities, remove inactive accounts, and mandate Multi-Factor Authentication (MFA) for privileged users.
- Malware Detection: Perform file system scans, code reviews, and network analysis to identify and remove malicious code.
- Backup Procedures: Create frequent, off-site, encrypted backups. Regularly test restoration to ensure data integrity and recoverability.
- SSL/TLS Security: Use modern protocols (TLS 1.2/1.3), strong cipher suites, and HSTS to secure data in transit.
- Professional Audit: A comprehensive audit, such as the one provided by Računalničar, combines these elements into a cohesive security strategy.
Frequently Asked Questions
How often should a WordPress security audit be performed?
A full security audit should be performed at least annually. However, a lighter scan for vulnerabilities and malware should be conducted monthly. If a major update to the core, a theme, or a plugin is installed, a targeted audit of those components is recommended.
What is the difference between a vulnerability scan and a penetration test?
A vulnerability scan is an automated process that identifies known weaknesses. A penetration test is a manual, in-depth assessment where a security professional attempts to exploit those weaknesses to demonstrate real-world risk. A penetration test provides a deeper understanding of the impact of vulnerabilities.
Can a security audit guarantee that my site will never be hacked?
No security measure can guarantee absolute protection. However, a comprehensive audit significantly reduces the risk of compromise by identifying and mitigating known vulnerabilities. It also provides a framework for ongoing security monitoring and response.
What tools are used for WordPress security audits?
Common tools include vulnerability scanners like WPScan, malware scanners like Wordfence, and penetration testing frameworks like Kali Linux. Professional auditors often use a combination of automated tools and manual techniques to ensure thorough coverage.
Is Multi-Factor Authentication (MFA) mandatory for all users?
MFA is strongly recommended for all users, but it is critical for privileged users such as Administrators and Editors. For regular subscribers or contributors, MFA may be optional depending on the sensitivity of the data they can access.
How does Računalničar approach WordPress security audits?
Računalničar uses a combination of Kali Linux and WebTesterAI MCP to perform agent-orchestrated security tests. This approach allows for deep, automated analysis of vulnerabilities and malware, providing a detailed report with actionable recommendations.
What should I do if a security audit finds critical vulnerabilities?
Immediately isolate the affected components, apply patches or updates, and change all passwords. If malware is detected, restore from a clean backup. Work with a security professional to remediate the issues and implement additional controls to prevent recurrence.
Does a security audit cover the hosting environment?
A comprehensive audit should include an assessment of the hosting environment, including server configuration, firewall rules, and network security. However, the scope of the audit should be clearly defined to include or exclude specific hosting components.
Conclusion
A WordPress security audit is a multi-faceted process that goes beyond simple plugin updates. It requires a deep understanding of configuration, access control, malware, backups, and encryption. By addressing each of these areas systematically, you can significantly reduce the risk of a security breach. Računalničar, Sebastijan Bandur s.p. offers professional security testing services that leverage modern tools and methodologies to provide a comprehensive assessment of your WordPress site. To schedule an audit, start your inquiry today.